Problem
It is 5pm on a Friday and someone has lost a laptop. Now what?
Seventy-two hours is not long when the first six are spent working out who is in charge and which systems were involved. Predefine the roles, start the clock at detection and log every decision as it is made, so the notification is evidenced rather than reconstructed.
From £500/month · 12-month agreement · All launch modules included
Trusted by privacy teams at
“The regulator will ask what you knew, when you knew it, and what you did in between.”
In the platform
The shape of your incidents, before the next one.
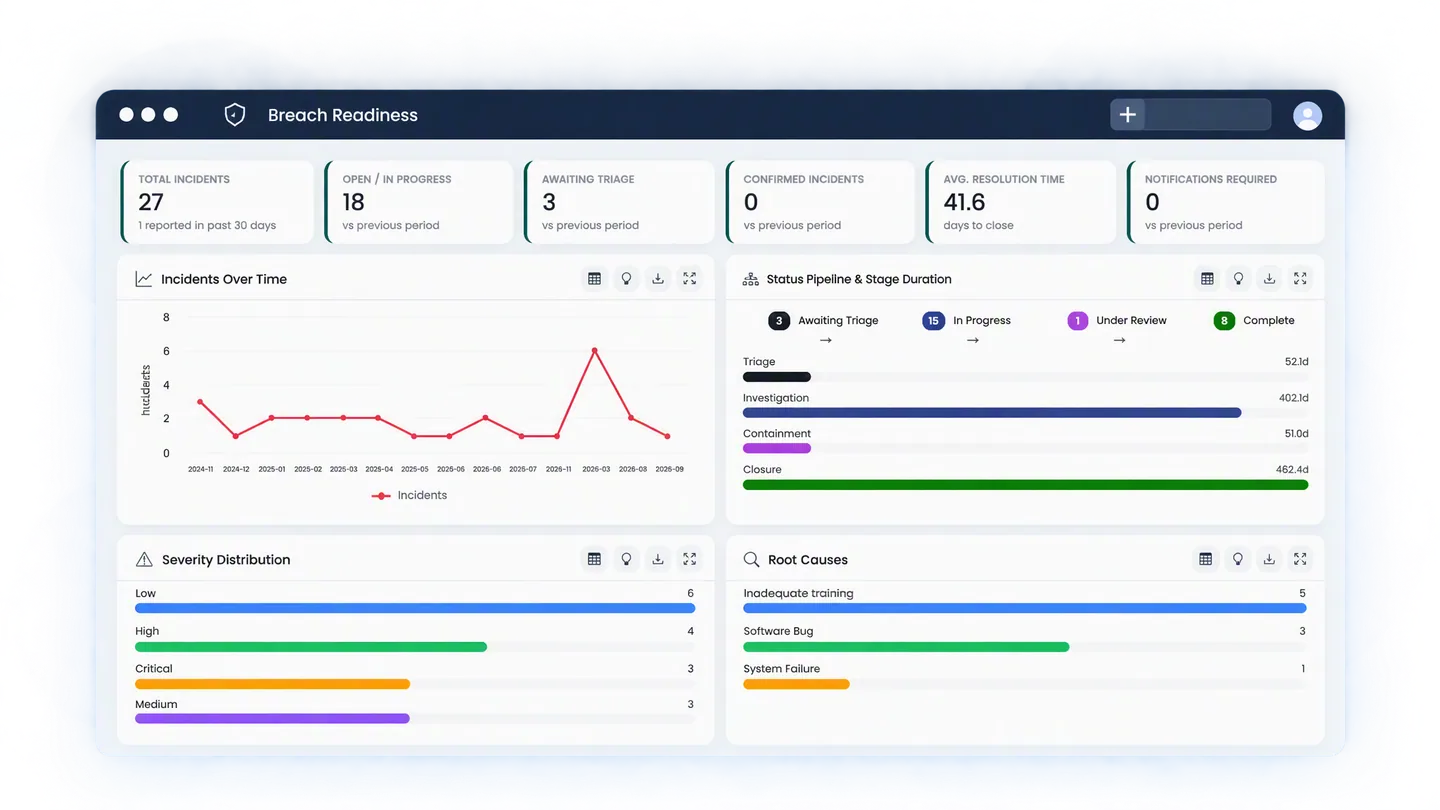
This is the breach readiness view. The top row is the current position: incidents open, how many are still awaiting triage, how many have been confirmed and how many have crossed the threshold for notifying a regulator. Below it, the pipeline shows where cases are stacked up and how long each stage is taking in practice, from triage through investigation and containment to closure. Severity and root cause sit alongside, so the pattern behind the incidents is something you can point at rather than something you suspect.
Functionality
Rehearsed, not improvised.
01
Roles set before the incident
Triage lead, DPO, comms and legal are named in advance, each with a fallback, so nobody is deciding who decides at 5pm on a Friday.
02
The clock starts at detection
Every action is timestamped against the 72-hour deadline, so you always know how much runway is left and can show how you used it.
03
Blast radius from the map
Link the incident to the systems involved and the estate shows the processing activities, vendors and data subjects affected.
Clear pricing
Clear pricing for privacy management software.
Choose the plan that matches your headcount and needs. Every one comes with the full set of launch modules.
-
Employees
Up to 750
from
£500 /month
£6,000 billed annually
- 10 user accounts
- All launch modules
-
Employees
Most teams start here
751–1,500
from
£800 /month
£9,600 billed annually
- 25 user accounts
- All launch modules
- Assisted onboarding
-
Employees
1,501–3,000
from
£1,250 /month
£15,000 billed annually
- 50 user accounts
- All launch modules
- Assisted onboarding
-
Employees
3,001–5,000
from
£1,667 /month
£20,000 billed annually
- 100 user accounts
- All launch modules
- Assisted onboarding
-
Employees
Enterprise
5,000+ or complex groups
POA
Price on application
- User accounts to suit
- Multi-entity, multi-jurisdiction
- Procurement & security review support
What “from” covers
Prices assume a single legal entity operating in GDPR-focused jurisdictions (UK GDPR and EU GDPR).
What can increase the price
Multiple legal entities, additional jurisdictions beyond GDPR, or more user accounts than your plan includes, SSO integration. We’ll confirm your price in a written quote before you commit.
Terms
12-month agreement. All launch modules included. Billing terms confirmed in the order form.
Next step
Rehearse the Friday breach before it happens.
Book a demo to see the roles, the 72-hour clock and the evidence log working together on a live incident walkthrough.
25 minutes · Live walkthrough of the platform